Payment fraud is becoming faster, more automated and increasingly difficult to distinguish from legitimate activity. At the same time, artificial intelligence (AI) is beginning to change not only how fraud is committed, but also how consumers shop and make payments.
According to Cyril Lalo, CEO and founder of Ellipse, a member of International Card Manufacturers Association (ICMA), these developments expose a fundamental weakness in online payments: static card credentials can remain valuable to criminals long after they are stolen.
“The defense that survives improving AI is not better recognition of the attacker,” Lalo said. “It is removing the value of what the attacker steals, so that a breach produces data with no residual worth.”
Fraud Becomes More Automated
Fraud has increasingly migrated away from physical payment channels and toward digital transactions. Lalo identifies credential enumeration and automation as two developments that deserve particular attention.
Through enumeration attacks, criminals use software to test combinations of card numbers, expiration dates and security codes until they identify valid credentials. Automation enables them to conduct these attacks at a scale and speed that would not be possible manually.
Artificial intelligence could accelerate the threat further by making social engineering more convincing and accessible. Criminals can use AI to create fluent, localized messages, personalize attacks and imitate voices or faces. ICMA member Entrust’s 2026 Identity Fraud Report found that deepfakes now account for one in five biometric fraud attempts, illustrating how quickly synthetic identity tools are advancing.
“Almost anything a person can show to prove they are real, a machine may now imitate,” Lalo said. “Most fraud systems work by learning what normal customers look like, and that gets weaker as software gets better at looking normal.”
Bringing the Physical Card Back Into the Transaction
The physical EMV® card already contains a secure chip, issuer-personalized cryptographic keys and the ability to generate unique values that an issuer can verify. These capabilities allow the chip to participate actively in card-present transactions.
Online, however, the card is often represented by static information: the card number, expiration date and security code.
“The card number, expiry date and security code are largely static,” Lalo said. “Once copied, they can be reused.”
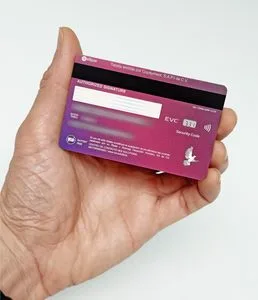
The printed security code illustrates the challenge. Although it is intended to demonstrate that the customer possesses the card, the code may remain unchanged for years and is frequently entered into merchant websites.
Risk scoring, tokenization, one-time passcodes and 3-D Secure help compensate for this weakness, but additional authentication can also introduce friction, false declines and abandoned purchases. Ellipse’s approach is to strengthen the credential itself by using the card’s EMV security foundation to generate a changing verification code.
“For manufacturers, this changes the role of the card,” Lalo said. “It stops being simply a carrier of credentials and becomes part of the security architecture.”
Greater Security Without an Unfamiliar Experience
Fraud prevention often requires issuers to balance security with convenience. Every additional message, redirect or authentication challenge may provide more confidence, but it also creates another point at which a legitimate customer could abandon the transaction.
A dynamic security code is designed to preserve the familiar checkout experience. The cardholder still looks at the card and enters three digits, but the code changes periodically rather than remaining valid for years. Previously stolen information therefore becomes less useful.
“The customer’s behavior does not change,” Lalo said. “But the issuer receives a stronger signal, which can allow its risk engine to challenge fewer transactions, not more.”
This approach could also help reduce false declines. When a legitimate purchase is rejected, the customer may complete the transaction with another card and potentially move future spending to that issuer.
“The objective should not be more authentication,” Lalo said. “It should be more confidence with less authentication.”
Confirming Human Intent in Agentic Commerce
The growing use of AI shopping assistants introduces another security question: How can an issuer determine whether a human authorized a transaction when software performs the shopping?
An AI agent may be authorized to search for a product, compare prices, select an item and fill a shopping cart. However, the agent could exceed its instructions, select the wrong product or become compromised. Possession of stored card credentials does not necessarily demonstrate that the cardholder intended a specific purchase.
Ellipse explored this challenge by building an autonomous shopping assistant that can find a product, fill a cart and proceed to checkout. At the final step, the assistant requires the cardholder to read and provide the current three-digit code from the physical card.
According to Lalo, the demonstration used a real prepaid Visa card equipped with a live Ellipse EVC® chip. The card was issued by Copayment, Ellipse’s issuing and processing partner in Mexico, through the NOI Solutions program. The test involved real authorization messages rather than a closed-loop simulation.
“The agent shops, the issuer verifies, and the transaction cannot be completed until a human reads the current code from the card,” Lalo said.
Watch Ellipse’s demonstration of an AI shopping agent completing an online purchase.
For the cardholder, this creates a way to retain control over the final authorization, even if the agent has access to other payment information. For the issuer, the current code can provide an additional signal that a person participated in approving the purchase.
Preparing for Credentials That Are Current, Not Merely Correct
Lalo expects payment security to move toward credentials that function as a changing state rather than a fixed collection of numbers.
“Today, card security data is checked for correctness,” he said. “Within the coming years, the question will increasingly be: Is this credential fresh, and did the cardholder intend this transaction?”
AI-driven commerce will accelerate that transition because human presence and intent may no longer be inferred reliably from a device, browser or agent platform.
Preparing for this environment will require action across the card ecosystem. Manufacturers can explore how cards can participate more actively in digital security. Issuers can begin testing dynamic credentials and evaluating the validation capabilities required from their processors. Technology providers can develop payment experiences that allow AI agents to assist consumers while still providing a secure way to bring the cardholder into the final authorization.
The unresolved question of responsibility will also demand attention. Existing payment rules were not designed for autonomous software that may have permission to use a card but makes a purchase the cardholder did not intend.
The industry will need mechanisms that distinguish access to a payment credential from approval of a specific transaction. Dynamic credentials help establish that distinction by allowing the agent to perform the shopping while the cardholder retains control of the final payment decision.
“It is a subtle shift, from asking whether a credential is correct to whether it is current,” Lalo said. “But it is a fundamental one for payment security.”
ICMA Membership: Extending Industry Visibility
As an ICMA Gold Distinguished Partner, Ellipse is among the member companies demonstrating how innovation across the global card ecosystem continues to address emerging challenges in payments and security. ICMA’s Distinguished Partner Program provides participating companies with expanded opportunities for year-round visibility, industry engagement and connection across the card manufacturing community.
That visibility extends across ICMA’s communications and member resources. Ellipse’s profile in the ICMA Public Member Directory highlights its EVC® dynamic card security code technology, making information about the company’s capabilities accessible to industry professionals searching for products, services and potential business partners.
ICMA has also followed the evolution of EVC through its industry communications. In the August 2026 issue of Card Manufacturing magazine, Member & Product News highlighted the integration of Ellipse’s EVC technology with the Entrust Digital Card Solution and its potential application across physical cards, virtual cards and mobile wallets as agentic commerce develops.
Through resources such as the Public Member Directory, Card Manufacturing magazine and industry news, ICMA gives members opportunities to share innovations, increase visibility and demonstrate thought leadership across the global card industry. Members can also strengthen technical expertise and leadership skills through professional development programs such as Advanced Card Education (ACE), while events including EXPO and CardTREX provide opportunities to learn, connect and explore emerging technologies. Industry recognition through the Élan Awards of Excellence further showcases the innovation and achievements of ICMA members worldwide.